Azure architecture template
Azure AKS baseline cluster
Private AKS cluster behind Application Gateway WAF, with egress through Azure Firewall, Container Registry and Key Vault.
Free to start. Updated .
When to use it
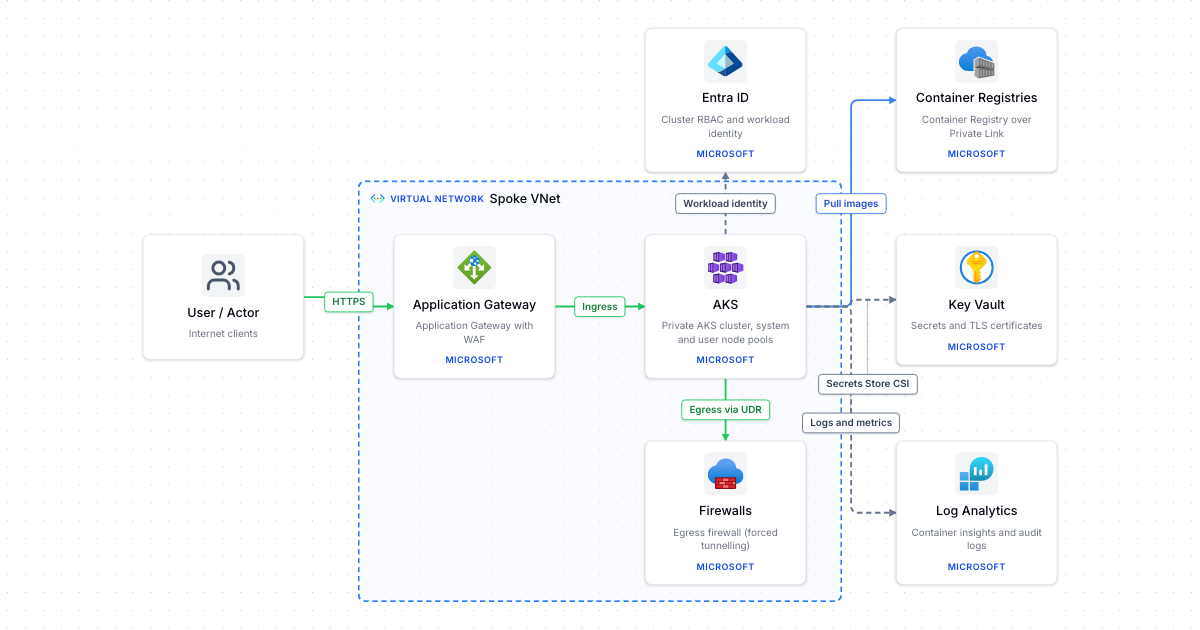
This template follows the shape of Microsoft's AKS baseline reference architecture, trimmed to the parts you need to explain the design. Internet traffic enters through Application Gateway with Web Application Firewall rules and reaches the private AKS cluster through an ingress controller. Outbound traffic is forced through Azure Firewall with a user-defined route, so the cluster can only call the destinations you allow. Images come from Azure Container Registry over Private Link, and pods read secrets and certificates from Key Vault with the Secrets Store CSI driver and Entra workload identity.
The baseline is secure by default but carries a lot of moving parts and a steady monthly cost before any workload runs. It suits regulated workloads and shared platforms. For a single team or a proof of concept, Azure Container Apps gives you containers without running the cluster. Send container insights and Kubernetes audit logs to Log Analytics from the start.
What's in this template
 User / ActorInternet clients
 Entra IDCluster RBAC and workload identity
 Application GatewayApplication Gateway with WAF
 AKSPrivate AKS cluster, system and user node pools
 FirewallsEgress firewall (forced tunnelling)
 Container RegistriesContainer Registry over Private Link
 Key VaultSecrets and TLS certificates
 Log AnalyticsContainer insights and audit logs
How it connects
- User / Actor → Application Gateway (network): HTTPS
- Application Gateway → AKS (network): Ingress
- AKS → Container Registries (data): Pull images
- AKS → Key Vault (dependency): Secrets Store CSI
- AKS → Entra ID (dependency): Workload identity
- AKS → Firewalls (network): Egress via UDR
- AKS → Log Analytics (dependency): Logs and metrics
More Azure templates
Azure 3-tier web app
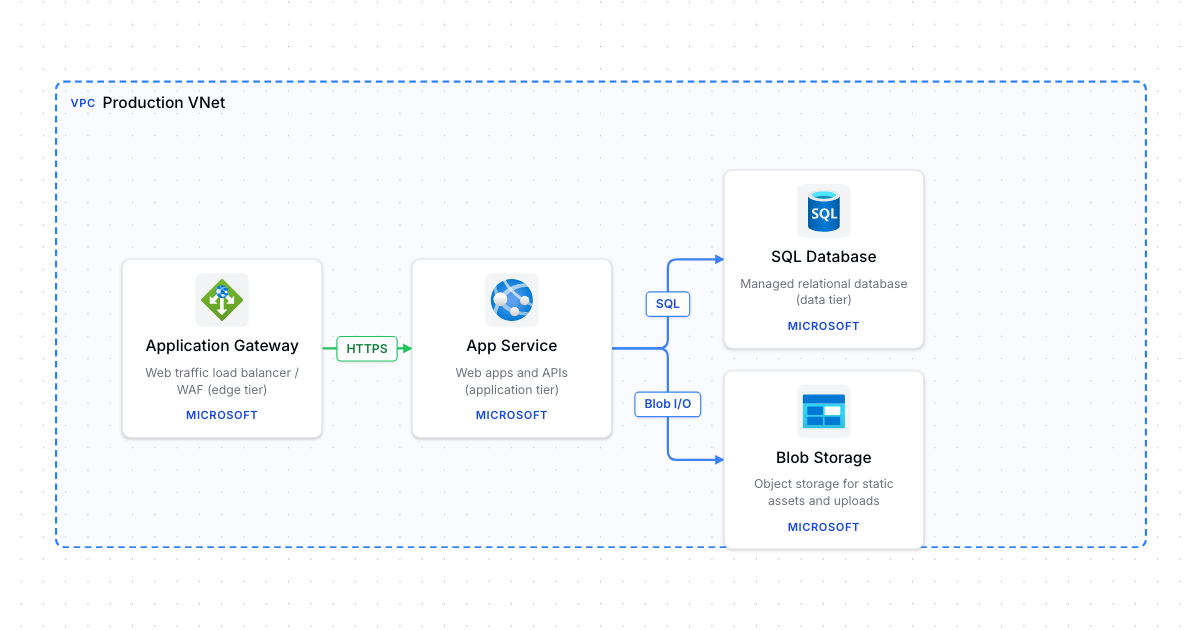
Edge -> application -> data tier inside a VNet: Application Gateway, App Service, SQL Database and Blob Storage.
Azure landing zone (starter)
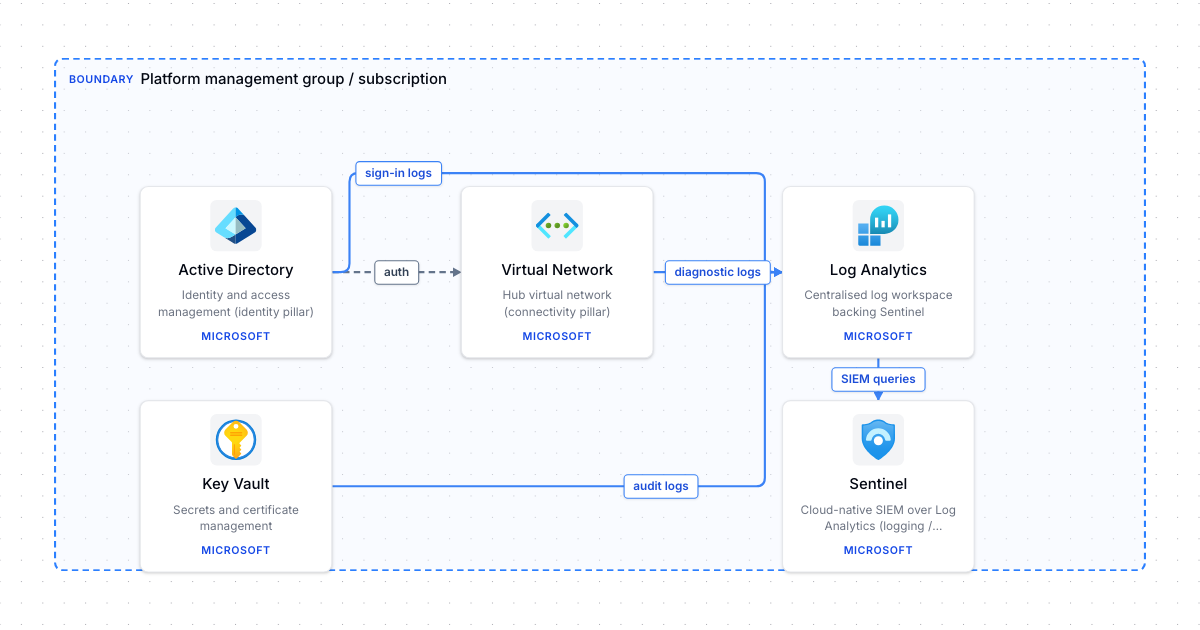
Starter platform landing zone: management-group scope with identity, hub networking, secrets and centralised logging.
Azure hub-spoke network
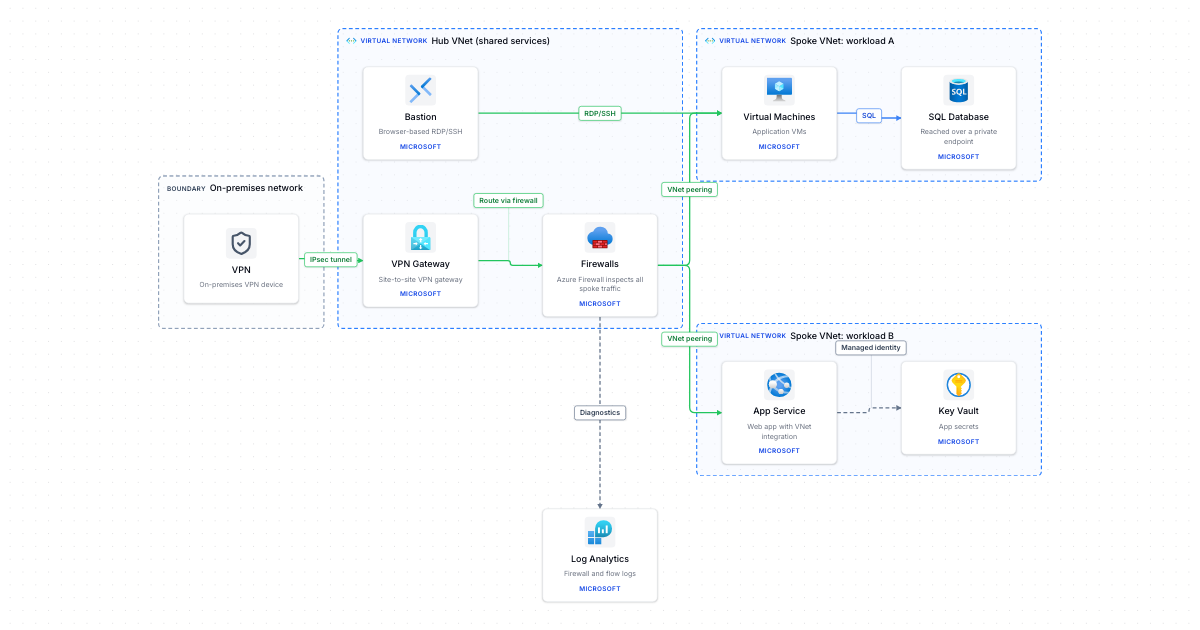
Hub VNet with VPN Gateway, Azure Firewall and Bastion, peered to two workload spokes, with on-premises connectivity.
Make it your own
Open a copy in the editor, then rename, rearrange and extend it.