Azure architecture template
Azure hub-spoke network
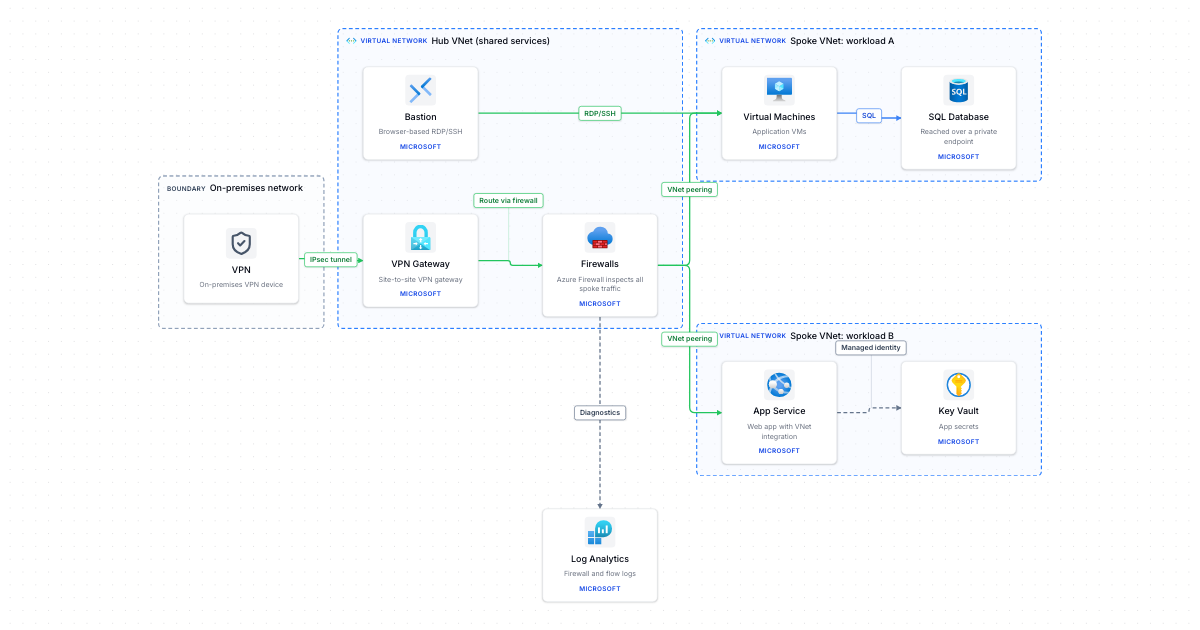
Hub VNet with VPN Gateway, Azure Firewall and Bastion, peered to two workload spokes, with on-premises connectivity.
Free to start. Updated .
When to use it
Hub-spoke is the standard Azure network topology once you have more than one workload or need a connection to on-premises. Shared services live in the hub: a VPN Gateway for the site-to-site tunnel, Azure Firewall to inspect traffic, and Bastion so administrators can reach virtual machines without public IP addresses. Each workload gets its own spoke VNet peered to the hub, and user-defined routes send spoke traffic through the firewall, which keeps spokes isolated from each other unless you allow a flow.
The firewall becomes a central control point and a central cost, and every new flow needs a rule, so agree who owns those rules early. Plan address spaces before you deploy, because peered networks cannot overlap and on-premises ranges count too. For many regions or branch offices, Azure Virtual WAN manages the hubs for you. Send firewall and flow logs to Log Analytics so you can see what is blocked.
What's in this template
 VPNOn-premises VPN device
 VPN GatewaySite-to-site VPN gateway
 BastionBrowser-based RDP/SSH
 FirewallsAzure Firewall inspects all spoke traffic
 Log AnalyticsFirewall and flow logs
 Virtual MachinesApplication VMs
 SQL DatabaseReached over a private endpoint
 App ServiceWeb app with VNet integration
 Key VaultApp secrets
How it connects
- VPN → VPN Gateway (network): IPsec tunnel
- VPN Gateway → Firewalls (network): Route via firewall
- Firewalls → Virtual Machines (network): VNet peering
- Firewalls → App Service (network): VNet peering
- Bastion → Virtual Machines (network): RDP/SSH
- Virtual Machines → SQL Database (data): SQL
- App Service → Key Vault (dependency): Managed identity
- Firewalls → Log Analytics (dependency): Diagnostics
More Azure templates
Azure 3-tier web app
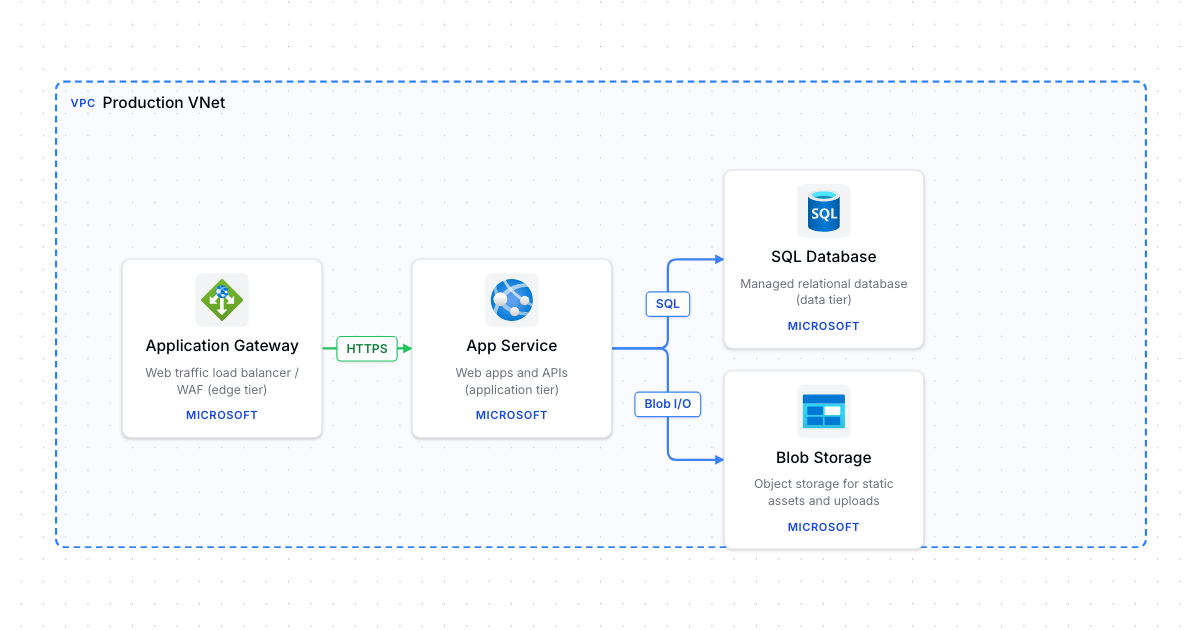
Edge -> application -> data tier inside a VNet: Application Gateway, App Service, SQL Database and Blob Storage.
Azure landing zone (starter)
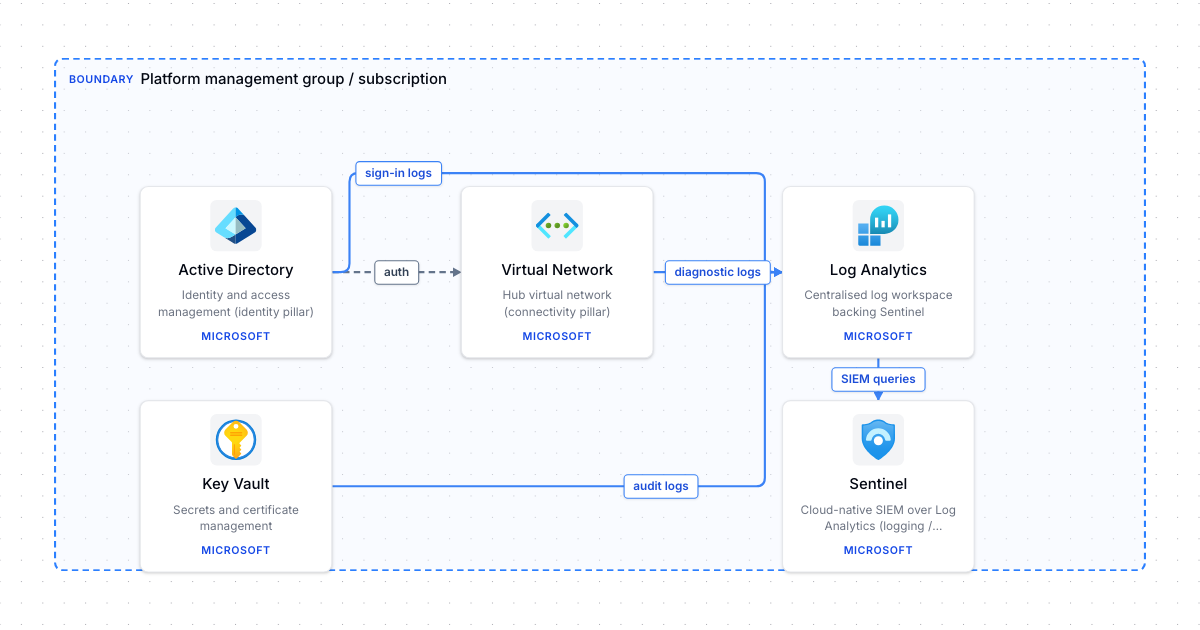
Starter platform landing zone: management-group scope with identity, hub networking, secrets and centralised logging.
Azure AKS baseline cluster
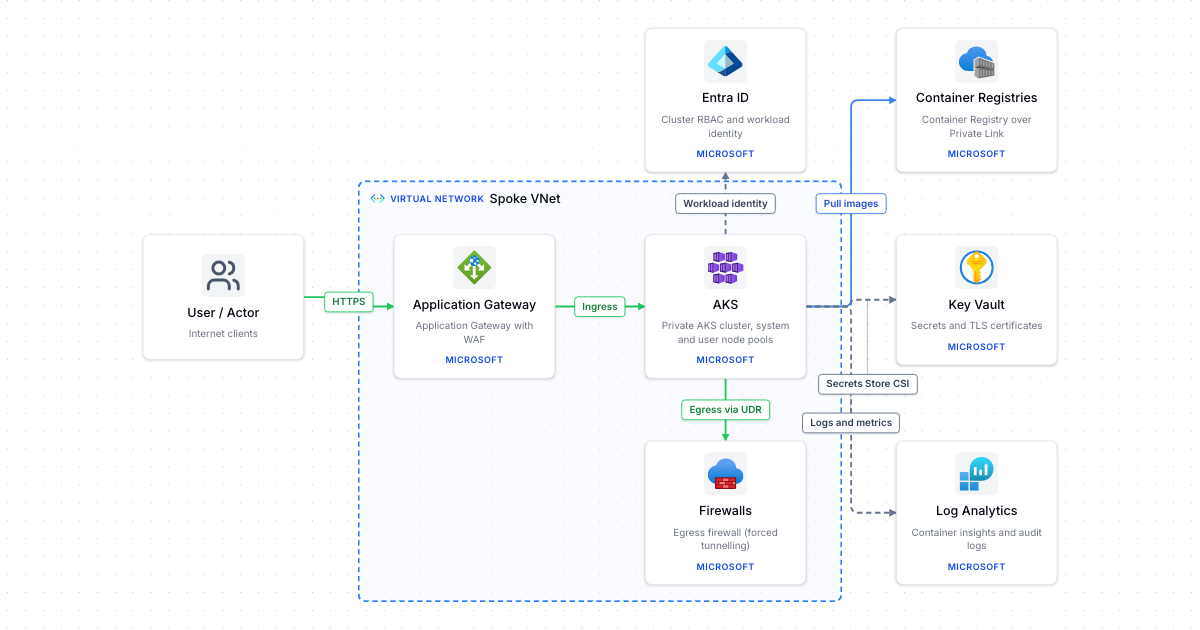
Private AKS cluster behind Application Gateway WAF, with egress through Azure Firewall, Container Registry and Key Vault.
Make it your own
Open a copy in the editor, then rename, rearrange and extend it.